Define branches, sub-branches, and units to manage your devices efficiently.
POEMS supports a hierarchical organizational structure to manage devices and operations.
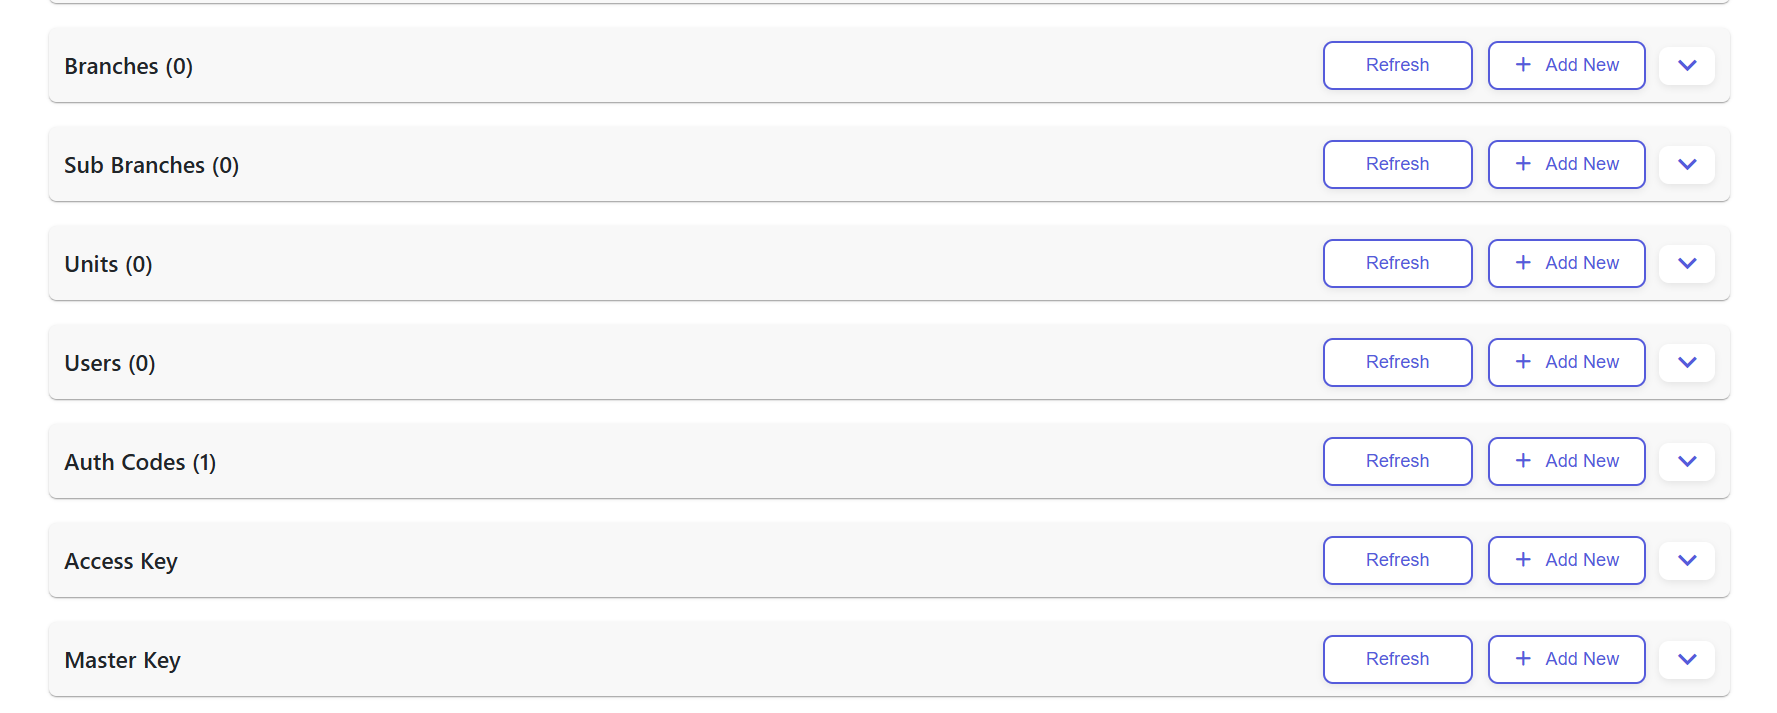
Each expandable row opens the corresponding module for branches, users, auth codes, access keys, or master key management.
Clicking Add New opens the creation form for the selected entity, such as a branch, unit, user, or credential record.
Refresh reloads the latest saved hierarchy records from POEMS without changing the current configuration.


Use the branch screen to create top-level groupings; the next visible state is the updated branch list with mapped operational regions.
Creating a sub-branch opens a child-level form under the selected branch and returns to the branch tree after save.
Adding a unit creates the most granular mapping level and becomes available for user assignment and device mapping in the next step.
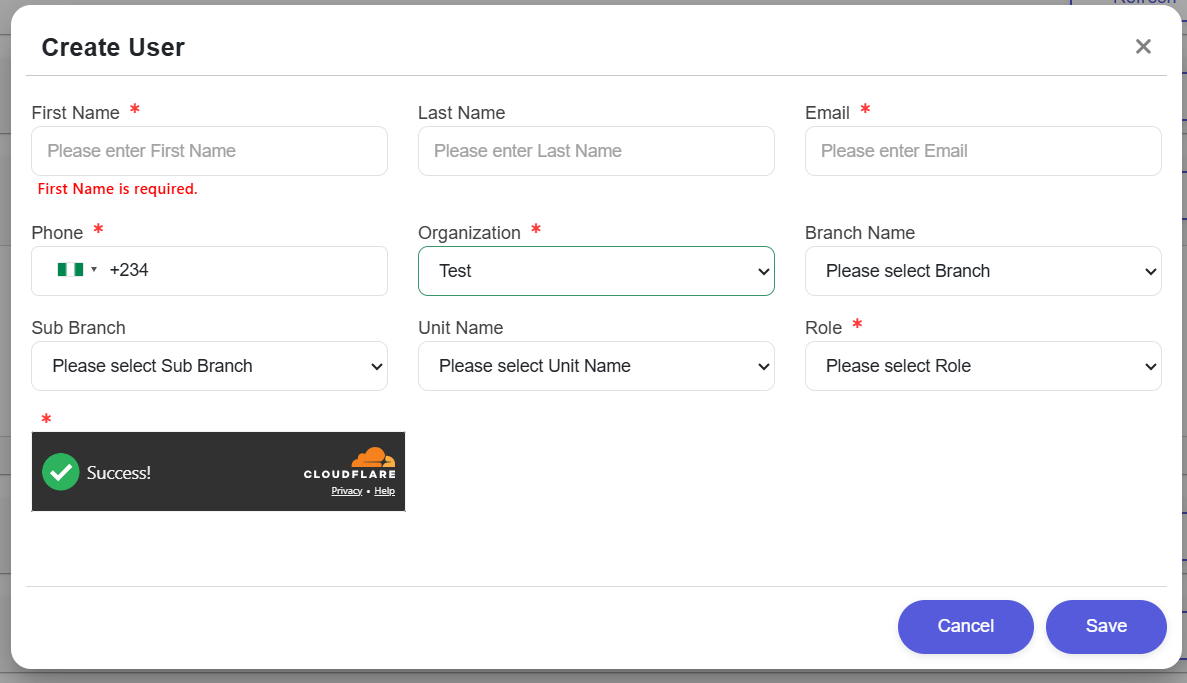
Selecting organization, branch, sub-branch, unit, and role determines exactly where the user will operate after creation.
Save creates the user and returns to the user list where the newly assigned role and hierarchy mapping can be reviewed.
Cancel closes the form and returns to the previous user-management screen without storing any changes.
| Entity | Description |
|---|---|
| Branches | Logical grouping of devices or operations. |
| Sub-Branches | Optional grouping under branches. |
| Units | Micro-level grouping (optional). |
| Users | System users with assigned roles. |
| Auth Codes | Used for transaction classification / authorization. |
| Access Keys | Used for API authentication (HMAC headers). |
| Master Key | Root credential (only Super Admin can generate). |
Top-level logical grouping for broad operational oversight.
Intermediate level for city management.
The most granular level for specific soundbox clusters.
| FI Responsibility | Payvala Responsibility |
|---|---|
Maintain accurate mappings between merchants, devices (deviceSn) and organizational units. |
Provide POEMS functionality to manage hierarchy, users and device registration. | Ensure only authorized users manage device assignments and credential operations. | Enforce RBAC restrictions for organizational actions. |